


Cybersecurity is an ongoing investment, and it’s essential to stay informed about the latest threats and best practices.
The digital age has transformed the way businesses operate, but it has also brought unprecedented cybersecurity challenges. Data breaches, ransomware attacks, and other cyber threats pose significant risks to businesses of all sizes. To safeguard your business, a comprehensive approach is essential.
Cybercriminals are constantly evolving their tactics, making it crucial to stay informed about the latest threats.
Common Cyber Threats
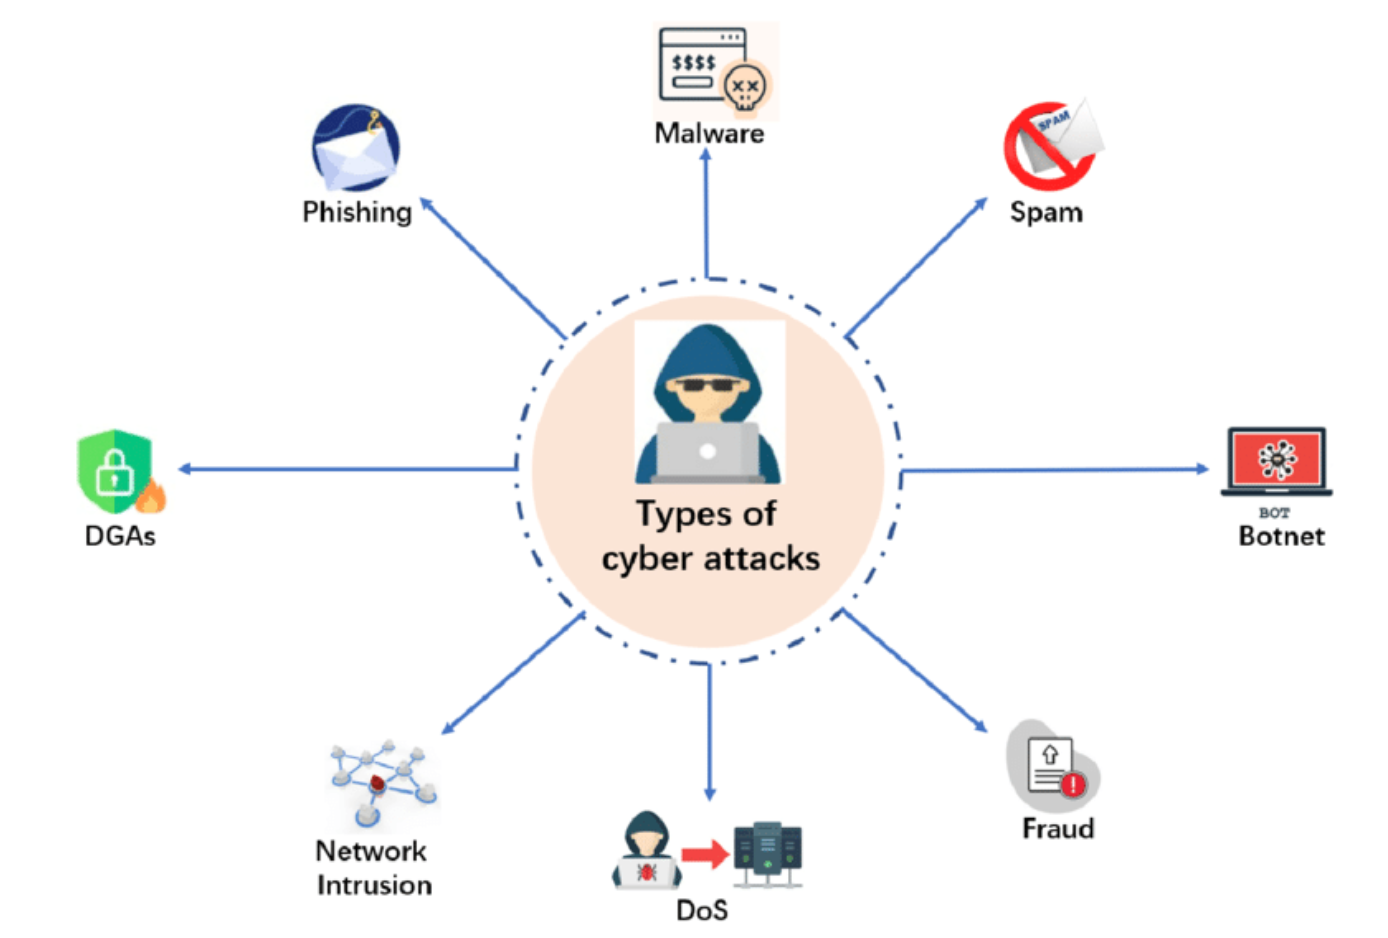
- Malware: Malicious software designed to infiltrate systems and damage or steal data. This can include viruses, worms, Trojans, spyware, and ransomware. Ransomware is a particularly insidious form of malware that encrypts files and demands a ransom for decryption.
- Phishing: Social engineering attacks that trick users into revealing sensitive information. Phishing attacks often come in the form of fraudulent emails or websites that mimic legitimate organizations. Techniques like spear phishing target specific individuals or organizations, increasing the likelihood of success.
- Data breaches: Unauthorized access to sensitive information. These can occur through hacking, insider threats, or accidental data exposure. The consequences of a data breach can be severe, including financial loss, reputational damage, and legal liabilities.
- Denial-of-service (DoS) attacks: Overwhelming a system with traffic to prevent legitimate users from accessing it. Distributed Denial-of-Service (DDoS) attacks involve multiple systems attacking a target simultaneously, making them particularly difficult to defend against.
- Insider threats: Employees or contractors who pose a security risk. This can include accidental data leaks, intentional data theft, or sabotage. Implementing strict access controls and employee training can help mitigate insider threats.
- Supply chain attacks: Targeting vulnerabilities in the supply chain to gain access to an organization’s network. These attacks often involve compromising a supplier or vendor to gain access to the target organization. Supply chain risk management is crucial for protecting against these threats.
Crafting Effective Cybersecurity Policies
A robust cybersecurity strategy involves multiple layers of protection. Here are some essential components:
Employee Training and Awareness
Your employees are the first line of defense. Regular cybersecurity training is crucial to help employees recognize and avoid phishing attempts, weak passwords, and other common threats. Key training topics include:
- Phishing awareness: Teach employees to identify and report suspicious emails or websites, including those with urgent or threatening language.
- Password security: Emphasize the importance of strong, unique passwords and avoiding password reuse. Encourage the use of password managers.
- Social engineering tactics: Educate employees about common social engineering techniques such as pretexting, tailgating, and baiting.
- Data handling and protection: Explain how to handle sensitive information, including proper storage, disposal, and avoiding unauthorized sharing.
- Incident reporting procedures: Outline steps employees should take if they suspect a security incident.
Network Security
Protecting your network is vital. Consider the following measures:
- Firewalls: Act as a barrier between your internal network and the internet. Implement both hardware and software firewalls.
- Intrusion Detection and Prevention Systems (IDPS): Monitor network traffic for suspicious activity and block potential threats.
- Virtual Private Networks (VPNs): Secure remote access for employees using strong encryption protocols.
- Access Controls: Implement strong password policies, role-based access controls, and multi-factor authentication.
- Network Segmentation: Divide your network into smaller segments to limit the impact of a potential breach.
- Network Monitoring: Continuously monitor network traffic for anomalies and suspicious activity using intrusion detection systems and security information and event management (SIEM) tools.
Data Protection
Safeguarding your data is paramount. Implement these measures:
- Data Encryption: Protect sensitive data with strong encryption algorithms both at rest and in transit.
- Data Backups: Regularly back up your data to multiple locations and test the restore process.
- Data Loss Prevention (DLP): Monitor and control the movement of sensitive information.
- Data Minimization: Only collect and retain the data necessary for your business operations.
- Data Retention Policies: Define clear policies for data retention and disposal.
Incident Response Plan
Develop a comprehensive incident response plan to address cyberattacks effectively. This plan should outline steps to contain the breach, mitigate damage, and recover from the incident. Include the following components:
- Incident identification and reporting procedures
- Incident response team roles and responsibilities
- Communication plan for stakeholders
- Data recovery and restoration procedures
- Post-incident review and improvement
Understanding Your Legal Obligations
First and foremost, understanding your legal responsibilities is key. If your business handles data from EU residents, GDPR compliance is essential. Non-compliance can lead to fines up to €20 million or 4% of your global turnover—whichever is higher. Ensuring GDPR compliance often requires a significant investment in data protection measures, highlighting the importance of financial discipline.
For businesses operating in California, the CCPA mandates transparency about data collection and usage. In 2022, over 200 enforcement actions were taken in California alone for non-compliance. The costs associated with adhering to these regulations and regularly updating your privacy practices are crucial investments in protecting your business’s reputation and financial health.
Key Regulations to Note:
- General Data Protection Regulation (GDPR): Requires businesses to implement rigorous data protection measures, conduct Data Protection Impact Assessments (DPIAs), and ensure data protection by design and by default.
- California Consumer Privacy Act (CCPA): Mandates transparency in data collection, providing consumers with rights to access, delete, and opt out of the sale of their personal data.
- Industry-Specific Regulations:
- HIPAA: For healthcare providers, mandates strict safeguards for patient information and prompt reporting of breaches.
- PCI DSS: For businesses handling credit card transactions, includes requirements for securing cardholder data and maintaining a secure network.
Technical Measures for Cybersecurity
Use Strong Encryption: Encrypting data is crucial for protecting it from unauthorized access. Implement end-to-end encryption for sensitive communications and use robust algorithms for stored data.
Implement Multi-Factor Authentication (MFA): MFA adds an extra layer of security by requiring users to provide multiple forms of verification. This could include something they know (a password), something they have (a security token or mobile device), and something they are (biometric verification).
Regularly Update Software and Systems: Keeping software and systems up-to-date is essential for defending against vulnerabilities. Regularly applying patches and updates helps protect against known threats.
Backup Data Regularly: Regular backups are vital for disaster recovery. Ensure that backups are frequent, stored securely, and regularly tested for data integrity and accessibility.
Infrastructure Monitoring: Regular infrastructure monitoring is crucial for identifying and addressing potential vulnerabilities in your IT systems. By continuously monitoring your infrastructure, you can detect and respond to threats before they escalate into serious issues. There are many tools like middleware.io, datadog, and Prometheus for monitoring.
Handling Cybersecurity Incidents
Even with robust defenses, breaches can still occur. That’s why having a well-defined incident response plan is essential. The Ponemon Institute’s 2023 report indicates that companies with a clear incident response plan face 50% lower breach costs. Investing in this plan can prevent significant financial fallout and help manage incidents effectively.
Legal requirements for breach notifications are also critical. A 2022 study found that businesses failing to meet these requirements faced fines averaging $500,000. Being financially disciplined means budgeting for potential costs and ensuring compliance to avoid hefty penalties.
Building a Culture of Cybersecurity
Foster a Security-Conscious Culture: Cultivating a culture where cybersecurity best practices are integral to daily operations is vital. Encourage employees to be proactive about data protection and create an environment where they feel comfortable reporting potential security issues.
Regular Security Audits: Conducting regular security audits helps assess the effectiveness of your cybersecurity measures. Deloitte’s 2023 audit report revealed that companies performing regular audits experienced 35% fewer successful attacks. Engaging external auditors can provide an objective evaluation and ensure compliance with industry standards.
Stay Informed on Emerging Threats: The cybersecurity landscape is constantly evolving. Stay updated on the latest trends and threats through industry reports and threat intelligence feeds. Adapting your security strategies to address new threats demonstrates a commitment to robust cybersecurity practices.
Conclusion
By combining these strategies, you can significantly reduce the risk of cyberattacks and protect your business’s reputation and bottom line. Remember, cybersecurity is an ongoing investment, and it’s essential to stay informed about the latest threats and best practices. By understanding your legal obligations, investing in robust policies and technologies, and maintaining a disciplined approach to budgeting and compliance, you can effectively safeguard your business against the ever-evolving landscape of cyber threats.


